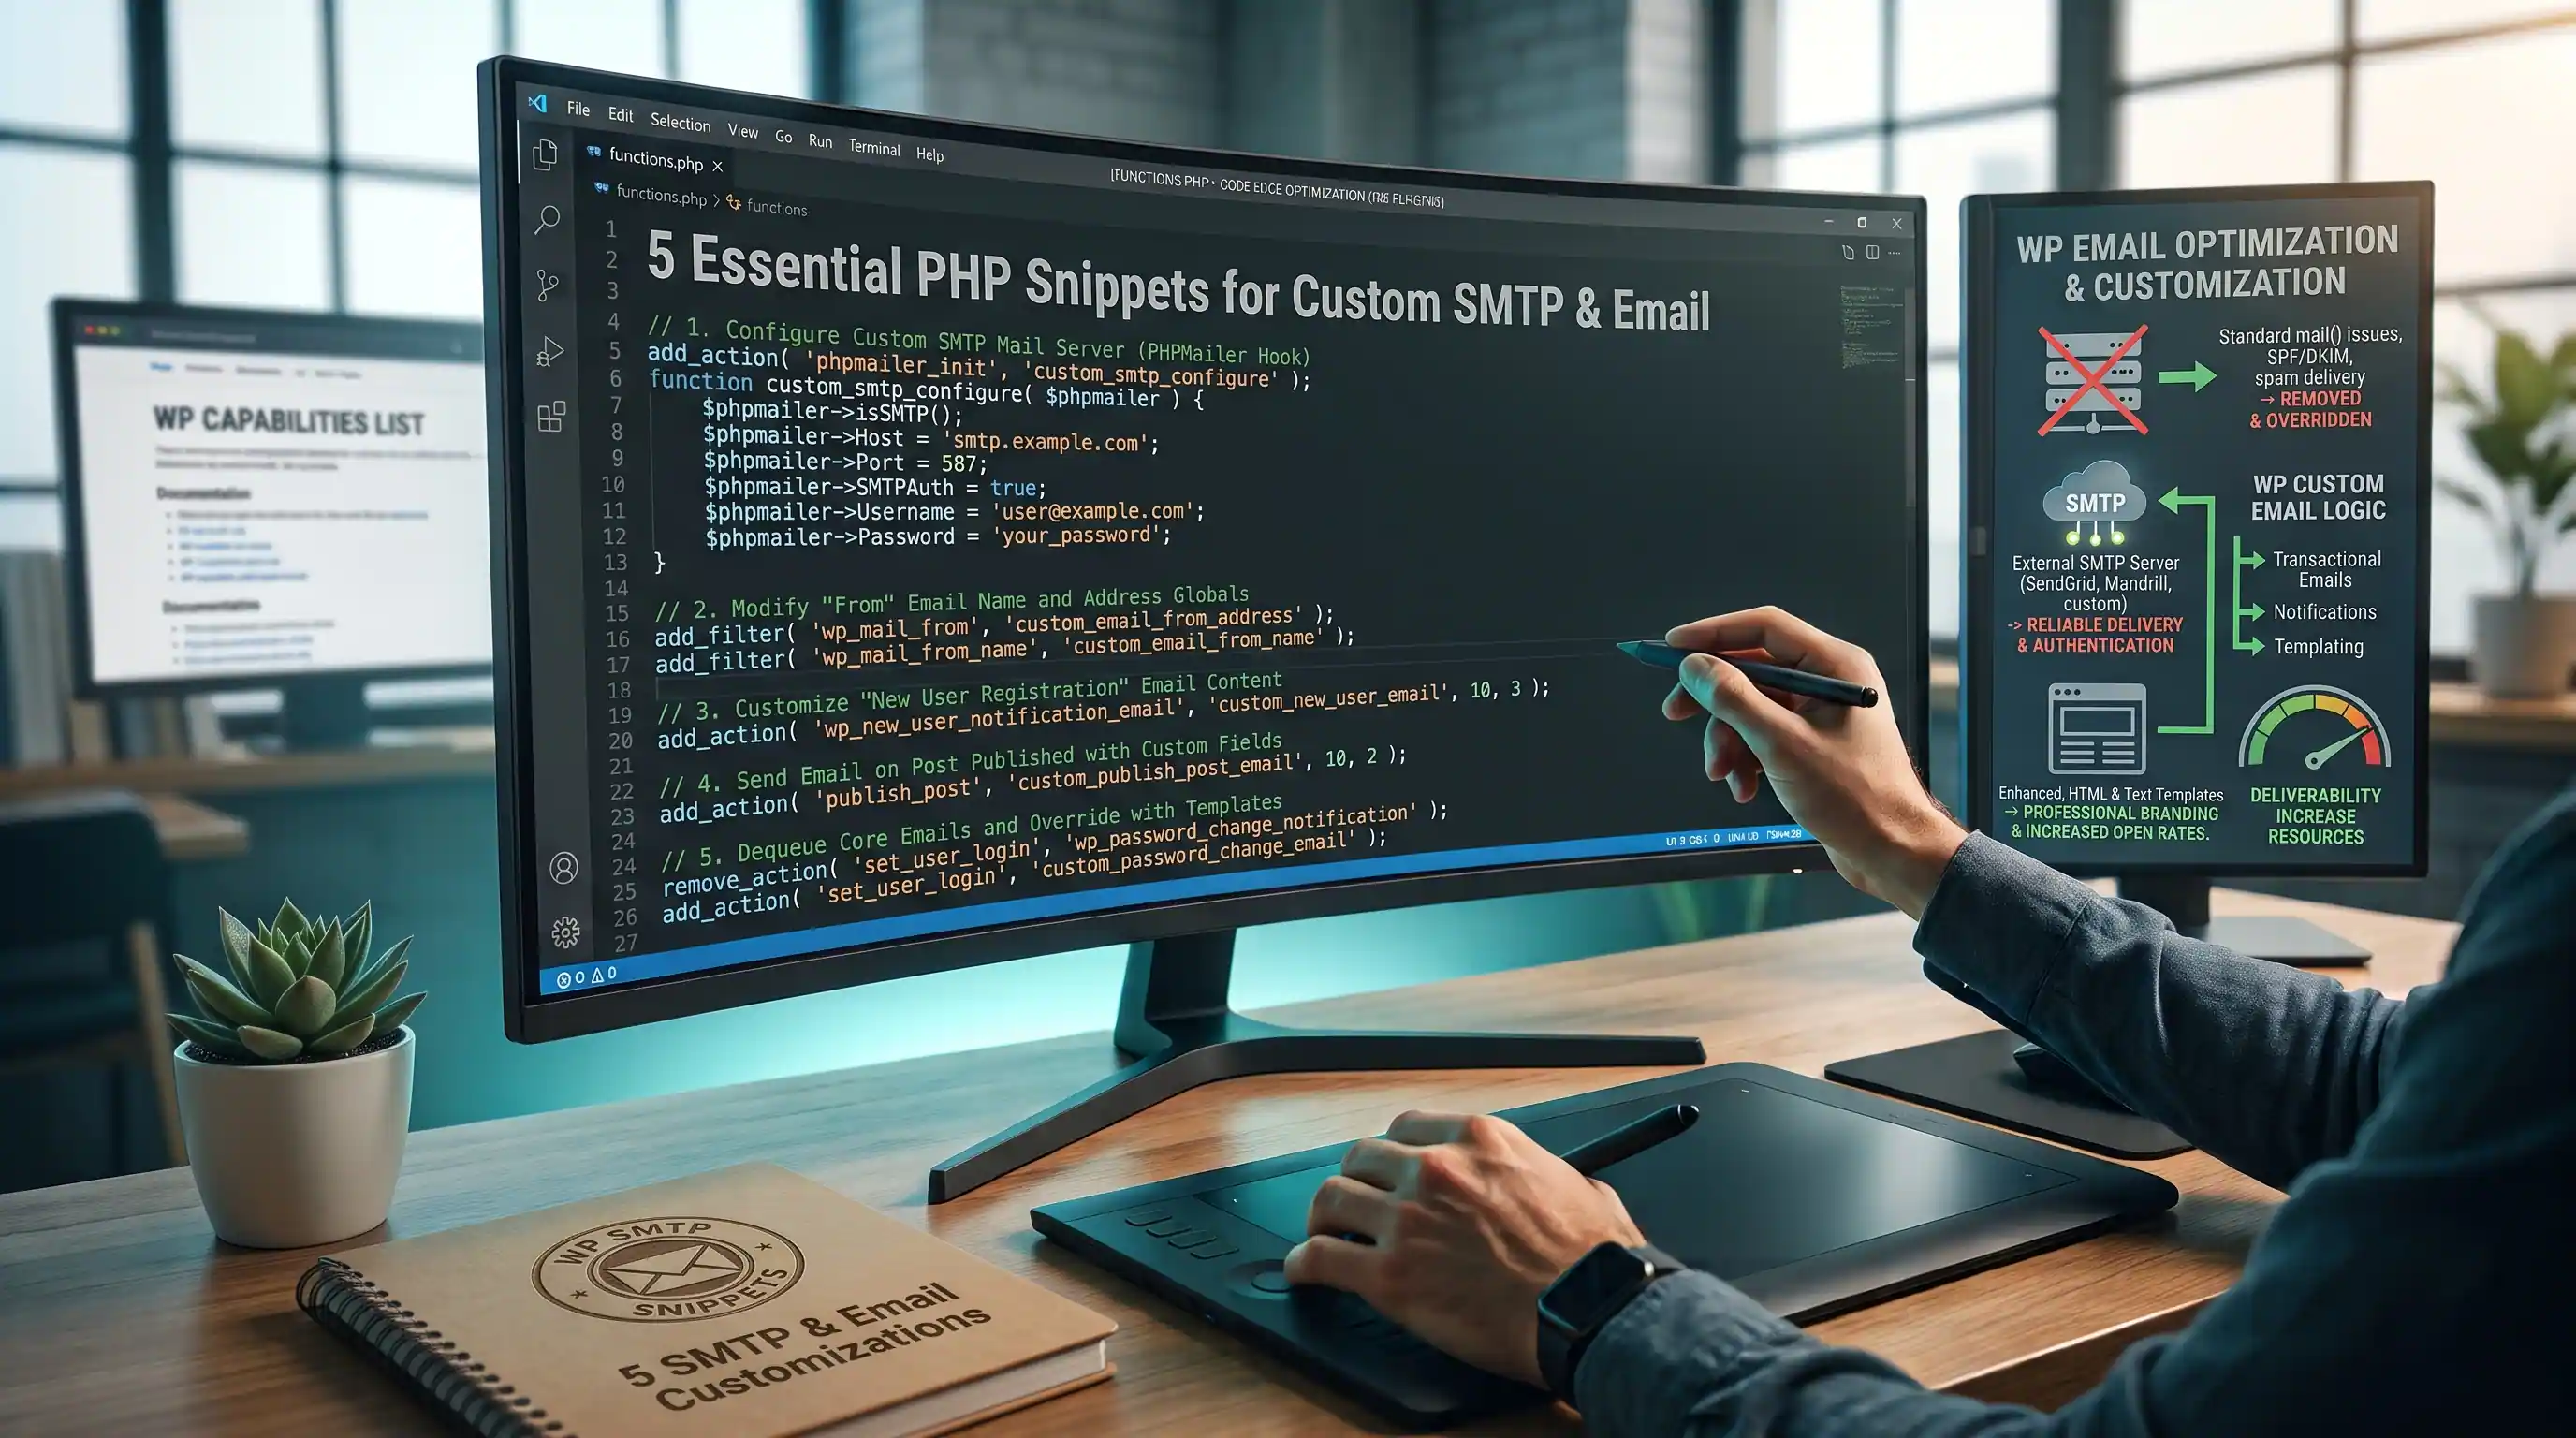
Why wp_mail() Alone Isn't Enough
WordPress's built-in wp_mail() sends through PHP's native mail() function by default — no authentication, no real sending domain reputation behind it, and most shared hosts either throttle it heavily or block it outright. That's why password reset emails vanish, contact form submissions never arrive, and order confirmation emails land in spam. A full SMTP plugin fixes this, but it also brings a settings UI, its own database options, and often a nag screen — when the actual fix is five WordPress core hooks you already have access to.
Add all five snippets to a site-specific plugin rather than your theme's functions.php, so mail configuration survives a theme switch. Create /wp-content/mu-plugins/custom-smtp.php, or drop these into an existing custom plugin.
A Word on Security Before You Start
Every SMTP snippet below needs a username and password for your mail provider. Never hardcode these directly in a plugin file that might end up in a public repository or get shared with a support ticket. Define them as constants in wp-config.php instead — a file that should already be excluded from version control on any properly configured project.
define('SMTP_HOST', 'smtp.yourprovider.com');
define('SMTP_USERNAME', 'your-smtp-username');
define('SMTP_PASSWORD', 'your-smtp-password');
define('SMTP_FROM_EMAIL', 'no-reply@yoursite.com');
Add these four lines to wp-config.php, above the /* That's all, stop editing! */ line, before using any of the snippets below.
1. Route All Mail Through Custom SMTP
phpmailer_init fires right before WordPress hands off an email to PHPMailer (the library wp_mail runs on internally), giving you a direct object reference to configure real SMTP authentication instead of the unauthenticated local mail() fallback.
Where to insert: your site-specific plugin file, after the wp-config.php constants above are in place.
- Paste the snippet below into your plugin file.
- Replace the port and encryption method with whatever your provider's documentation specifies (587 + TLS is the most common combination; some providers use 465 + SSL instead).
- Use a plugin like "WP Mail Logging" temporarily, or trigger a password reset email to yourself, to confirm mail is sending successfully.
- Check your mail provider's sending log/dashboard to confirm the message actually authenticated through SMTP rather than failing silently.
function configure_custom_smtp($phpmailer) {
    $phpmailer->isSMTP();
    $phpmailer->Host       = SMTP_HOST;
    $phpmailer->SMTPAuth   = true;
    $phpmailer->Port       = 587;
    $phpmailer->Username   = SMTP_USERNAME;
    $phpmailer->Password   = SMTP_PASSWORD;
    $phpmailer->SMTPSecure = 'tls';
    $phpmailer->From       = SMTP_FROM_EMAIL;
}
add_action('phpmailer_init', 'configure_custom_smtp');
2. Customize the Default Sender Email Address
Without this filter, WordPress defaults to sending from an address like wordpress@yourdomain.com — a mailbox that usually doesn't exist and that most SMTP providers will reject or flag unless it exactly matches an authenticated sending address on your account.
Where to insert: your site-specific plugin file.
- Paste the snippet below into your plugin file.
- Confirm the address matches (or is authorized to send as) the account you authenticated with in Snippet 1 — mismatched From addresses are a common reason SMTP providers reject mail outright.
- Send a test email and check the "From" field in your inbox.
function custom_wp_mail_from($original_email_address) {
    return SMTP_FROM_EMAIL;
}
add_filter('wp_mail_from', 'custom_wp_mail_from');
3. Customize the Default Sender Name
Left unchanged, outgoing WordPress emails show "WordPress" as the sender name in the recipient's inbox — not exactly reassuring for a customer expecting an order confirmation from your business.
Where to insert: your site-specific plugin file.
- Paste the snippet below into your plugin file.
- Replace "Your Site Name" with your actual business or site name.
- Send a test email and confirm the sender name shown in your inbox has updated.
function custom_wp_mail_from_name($original_email_from) {
    return 'Your Site Name';
}
add_filter('wp_mail_from_name', 'custom_wp_mail_from_name');
4. Force HTML Content-Type for Outgoing Emails
By default, wp_mail() sends plain text — any HTML markup in an email body renders as literal tags in the recipient's inbox instead of formatted content. This filter switches the content type globally so HTML in your email templates actually renders.
Where to insert: your site-specific plugin file.
- Paste the snippet below into your plugin file.
- Send a test email containing basic HTML (like a
<strong>tag) in the message body and confirm it renders as bold text, not literal tags.
function force_html_content_type() {
    return 'text/html';
}
add_filter('wp_mail_content_type', 'force_html_content_type');
One quirk worth knowing: this filter applies globally and stays active for every wp_mail() call on the request, including ones from plugins that expect plain text. If a specific email starts looking broken after this change, remove the filter right after your own wp_mail() call with remove_filter('wp_mail_content_type', 'force_html_content_type'); so it doesn't leak into unrelated emails sent later in the same request.
5. Disable Unnecessary Notification Emails
WordPress core sends more admin notification emails than most site owners realize — every new user registration and every password change generates one by default. On a site with frequent signups, that's a steady stream of noise. These two filters (both native to WordPress core, no deprecated hacks required) let you switch off each one independently.
Where to insert: your site-specific plugin file.
- Paste the snippet below into your plugin file.
- Register a test account and confirm the admin inbox no longer receives a "New User Registration" email.
- Change a test user's password and confirm no password-change notification email is sent.
- If you only want to disable one of the two, delete the corresponding
add_filter()line and keep the other.
// Stop notifying the admin about new user registrations
add_filter('wp_send_new_user_notification_to_admin', '__return_false');

// Stop sending the "your password was changed" notification email
function disable_password_change_notification($send, $user, $userdata) {
    return false;
}
add_filter('send_password_change_email', 'disable_password_change_notification', 10, 3);
Final Checklist
- SMTP credentials stored as constants in wp-config.php, not hardcoded in the plugin file.
- Test email sent and confirmed authenticating through SMTP via your provider's sending log.
- From address and sender name both confirmed correct in a received test email.
- HTML content confirmed rendering properly, with the content-type filter scoped if it affected other plugins' emails.
- Admin new-user notification and password-change notification confirmed disabled, or selectively kept as needed.
None of these five snippets touch a database table or need a settings page — they configure the exact same PHPMailer object an SMTP plugin would, just without the extra weight sitting on every admin page load in between emails.
Comments & Feature Requests
0 Found a bug, or want a new tool? Let us know below.
comments_no_comments